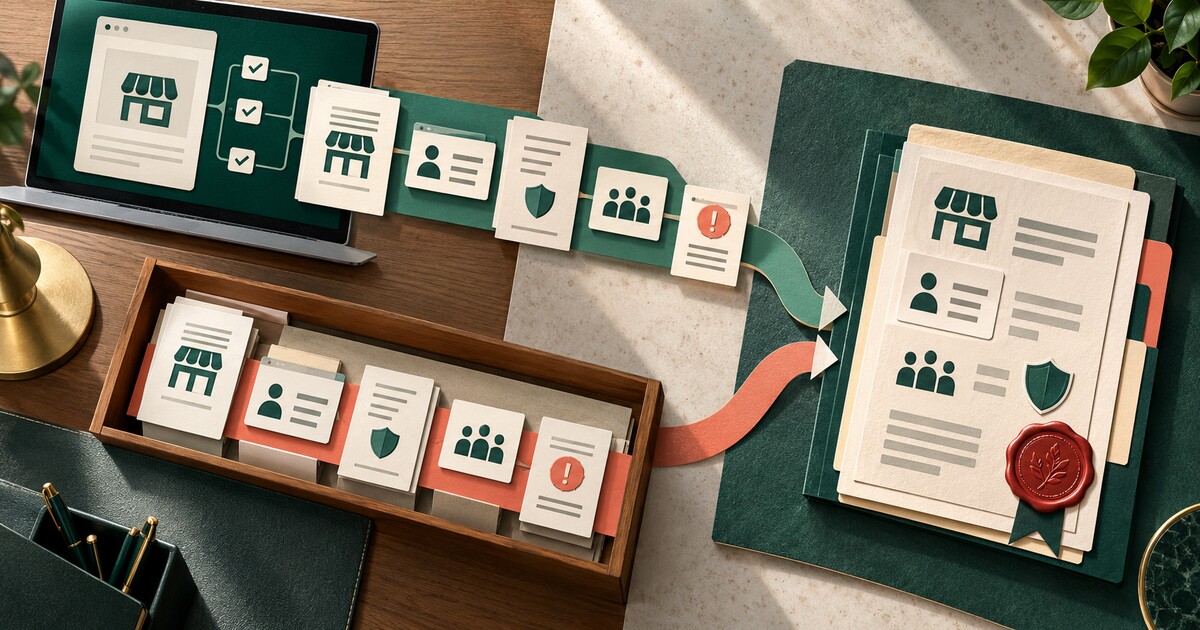
AI-assisted business account opening should produce one reconstructable evidence record across digital, branch and back-office channels—not three partial files and a final status. The record should distinguish entity identity, beneficial ownership, signer authority, purpose and expected activity, source documents, exceptions, human decisions and later updates.
This is an operations design, not a claim that AI changes the legal standard. AI can classify documents, extract fields, compare records and draft a review summary. Authorized employees remain responsible for resolving discrepancies, applying the credit union’s risk-based procedures and deciding whether the institution can form the required reasonable belief about the customer and relevant individuals.
Keep four identities separate
A business onboarding file can involve four different questions. What legal entity is opening the account? Which natural persons own or control it for customer-due-diligence purposes? Which people have authority to open or operate the account? And which employee or committee approved the relationship and any exceptions?
An AI extraction tool can blur those roles when names repeat across formation documents, ownership attestations, resolutions and identity records. The evidence record should therefore store each role separately, cite its source and show the verification result. A signer is not automatically an owner; an owner is not automatically an authorized signer; and the person completing the application may be neither.
FinCEN’s customer-due-diligence rule resource describes four core elements: identifying and verifying customers, identifying and verifying beneficial owners of covered legal-entity customers, understanding the nature and purpose of the relationship, and conducting ongoing monitoring. The rule’s beneficial-owner framework covers individuals with at least 25% ownership and one individual with significant control, subject to the rule’s definitions and exclusions.
Do not confuse BOI reporting with credit-union CDD
FinCEN’s 2026 changes make source labeling especially important. The agency’s final Corporate Transparency Act reporting rule exempts U.S. companies from filing beneficial-ownership information with FinCEN. That does not by itself erase a credit union’s separate CDD obligations when a covered legal-entity customer opens an account.
FinCEN also issued account-opening exceptive relief. A covered institution may limit identification and verification of beneficial owners to the first account, facts that call previous information into question, and circumstances required by its risk-based ongoing-due-diligence procedures. The relief is optional; institutions may retain their existing collection process.
The record should therefore state which authority and policy path applies: initial collection, permitted reliance on existing information, a trigger requiring refreshed information, or an exclusion. “Previously verified” is not enough. Preserve the prior record reference, the information relied upon, any confirmation, the trigger review and the employee decision.
Make the handoff visible
Business applicants often start online, add documents by email, call for help and finish in a branch. Each channel can create its own queue, notes and duplicate document set. AI can help reconcile them, but only if every item retains provenance: who submitted it, through which channel, at what time, for which entity and version, and whether staff accepted, corrected or rejected the extracted data.
Use a single case identifier from the first contact. When work moves between channels, create a handoff event rather than copying a summary. The event should show the open question, evidence already reviewed, responsible owner, due time and next permitted action. If the system cannot transfer the full record, stop automated progression and route the file to a controlled manual process.
Design the exception record before launch
Test deliberately difficult files: a recently converted entity, layered ownership, an unavailable beneficial owner, mismatched legal and trade names, a signer whose authority is unclear, an expired identity document, a changed address and a branch correction after digital submission. For each case, define who can resolve it, what evidence is acceptable, what requires escalation and what prevents account opening.
The exception record should preserve the original AI output, the discrepancy, supporting evidence, employee correction, approval and any restriction placed on the account. It should also capture false positives and repeated extraction errors so the credit union can decide whether to retrain, restrict or retire the tool.
Use the record after opening
The onboarding file becomes the baseline for monitoring and service. Changes in ownership, control, expected activity, business address or signer authority can be compared with that baseline. A later alert should link back to the relevant evidence instead of forcing investigators to reconstruct the original relationship from scattered systems.
The NCUA’s AI resources emphasize existing internal-control, risk-monitoring, resilience and third-party expectations. The voluntary NIST AI Risk Management Framework reinforces documented governance, measurement and response. Neither source prescribes this exact record; together they support an approach in which automation remains reviewable and accountable.
This onboarding design complements our coverage of the BOI-reporting and CDD distinction and the small-business lending control plan. One governs the relationship-entry evidence; the other governs underwriting and credit decisions. Keeping them connected but distinct prevents convenience from becoming ambiguity.
Build the shared evidence record before automating another onboarding step. Explore published CreditUnionAI Weekly web briefings for practical AI, compliance and operations coverage.
Browse web briefings