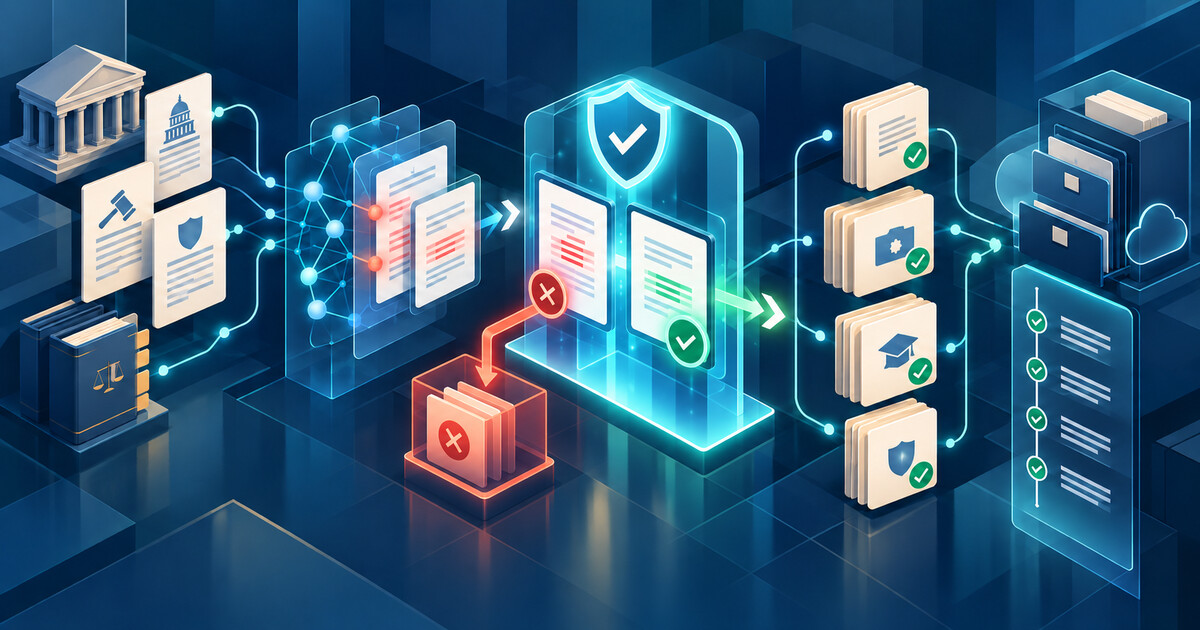
Policy maintenance is a plausible credit-union AI use case because the work is document-heavy and repetitive. A system can monitor official sources, compare versions, identify changed language, search an internal policy library and propose which procedures, disclosures, controls or training materials may need review.
The dangerous shortcut is to treat that proposal as the compliance decision. A new rule, interpretation, supervisory letter or state requirement rarely maps cleanly to one paragraph in one policy. Applicability may depend on charter, product, geography, threshold, effective date, contract, system behavior and facts that are not present in the source document. A generated redline can also look complete while missing the operational control that makes the policy true.
The NCUA’s AI resource, updated April 28, says existing technology-neutral requirements still apply and examiners evaluate internal controls, ongoing risk monitoring and vendor due diligence. The NIST AI Risk Management Framework gives organizations a govern-map-measure-manage structure for the AI layer. Official sources such as 12 CFR Chapter VII in the eCFR, the current Federal Register and NCUA letters and other guidance should remain the evidence base. Those sources support automation that organizes change—not automation that silently defines the credit union’s obligations.
1. Build an authoritative source register
Start with a controlled list of sources, not a broad web crawl. For each federal and state regulator, legislature, rule repository, supervisory body and binding agreement, record the official URL or feed, document type, jurisdiction, responsible owner, review frequency and escalation path. Separate binding law and regulation from guidance, speeches, enforcement examples, trade-association summaries and vendor commentary.
Capture the document itself or an immutable reference, not only a model-generated summary. A retrieval system should retain the title, issuing body, publication date, effective or compliance date, amendment history, docket or citation and the exact version reviewed. If a source changes without a new identifier, store the prior version and a content hash.
Evidence: source register, authority tier, monitored URL, retrieval time, document hash, superseded version and assigned regulatory owner.
2. Separate change detection from applicability
An AI system may detect that text changed and suggest affected topics. It should not determine that the change applies. Route every candidate through a documented applicability assessment covering charter, state, product, service, member segment, transaction, threshold, vendor role and effective date. Require the reviewer to cite the controlling text and explain both inclusion and exclusion.
Use deterministic rules for known triggers such as dollar thresholds, dates and product scope, but preserve a legal or compliance review for ambiguous language. When facts are missing, the system should create a question or exception—not fill the gap with an assumption.
Evidence: changed passage, proposed topic, applicability factors, missing facts, reviewer rationale, cited authority and decision date.
3. Map obligations to the operating system
Do not map a regulatory change only to policy documents. Connect each obligation to procedures, product requirements, system configurations, disclosures, forms, scripts, vendor controls, monitoring, training, testing and board or committee reporting. One source change may affect several owners; one control may satisfy several obligations.
Maintain a relationship record that answers five questions: What must happen? Who owns it? Where is it performed? What evidence proves it? Which upstream and downstream artifacts depend on it? That graph lets the AI propose a blast radius while leaving the accountable owner to confirm it.
Evidence: obligation identifier, policy and procedure links, control owner, system or vendor dependency, testing method and proof location.
4. Generate traceable redlines, not replacement prose
A drafting assistant should work from the approved current version and show additions, deletions and moved language. Every material proposed edit should cite the source passage and the mapped obligation. The system should also state what it did not update—for example, a procedure owned by another team or a disclosure managed in a separate platform.
Prohibit uncited legal conclusions, invented deadlines and silent harmonization of conflicting sources. Preserve house style, defined terms, cross-references and approval language. If the model cannot locate the current approved artifact, it should stop rather than draft against a stale copy.
Evidence: base version, complete redline, source-to-edit citations, unresolved conflicts, excluded artifacts, model version and prompt or workflow record.
5. Keep approval and publication authority human
Define who may approve legal interpretation, policy language, procedure changes, member communications, system configuration and training. Those are different authorities. The AI can assemble the packet and route it, but it should not approve, publish, attest or close the change.
Require separation of duties for material changes. At minimum, the subject-matter owner confirms the operational design, compliance or legal confirms the obligation, and the designated authority approves the artifact. Emergency changes need an explicit temporary path, expiration and retrospective review.
Evidence: approval matrix, reviewer comments, conflicts resolved, signed decision, publication time, emergency exception and follow-up due date.
6. Prove implementation beyond the document
A revised policy is not implementation. Create linked tasks for procedures, code or configuration, vendor changes, forms, notices, training, quality assurance, monitoring and testing. Set owners and dates from the actual compliance timeline, including any phased applicability or transition rules.
Before closure, sample the operating evidence. Confirm the published version is the approved version, staff can find it, affected systems behave as required, training reached the right population and monitoring can detect exceptions. Track overdue dependencies separately from completed drafting.
Evidence: implementation plan, owner acknowledgments, deployed configuration, training completion, test results, exception log and closure approval.
7. Preserve the audit trail and the manual path
Keep the source snapshot, extraction, change comparison, model output, reviewer edits, decisions, approvals, implementation evidence and superseded artifacts together. A reviewer should be able to reconstruct why the credit union concluded that a change did or did not apply and how that conclusion reached operations.
Test the manual process at least annually and after a material vendor or model change. Staff must be able to monitor priority sources, assess applicability, issue an urgent update and preserve evidence when the AI service is unavailable. Define stop conditions for missed official changes, stale source versions, uncited redlines, unauthorized publication, incomplete mappings and rising reviewer-correction rates.
Evidence: immutable event history, retention rule, access log, fallback exercise, correction metrics, stop decision and restart approval.
A minimum change-control packet
Compliance, legal, risk and operations leaders should be able to review one compact packet containing:
- the authoritative source, version, changed passages and relevant dates;
- the applicability decision, cited rationale and unresolved questions;
- the obligation-to-policy, procedure, system, vendor, training and monitoring map;
- traceable redlines and every human edit to the generated proposal;
- approvals by role and separation-of-duties evidence;
- implementation tasks, test results, exceptions and overdue dependencies; and
- the final effective package plus superseded versions and rollback instructions.
The packet should distinguish three dates that are often confused: when the source changed, when the credit union approved its response and when every affected control was operating.
Run five tests before launch
- Source test: modify a monitored page without changing its title and confirm the system captures a new version and alerts the right owner.
- Applicability test: present similar changes that apply to different charters, states or products and verify that missing facts become questions.
- Mapping test: seed one obligation that affects policy, system configuration, training and a vendor; confirm every dependency is identified.
- Authority test: attempt to publish an AI-generated redline without required approvals and confirm the workflow blocks it.
- Evidence test: reconstruct one completed change from source through operating control, then repeat the process with the AI service unavailable.
AI can reduce the mechanical burden of comparison and routing. It cannot carry the credit union’s accountability for legal interpretation or operational truth. The durable design keeps official sources authoritative, makes every inference reviewable, ties documents to controls and closes only when implementation can be proved.
Turn regulatory change into controlled implementation. Subscribe to the CreditUnionAI Weekly Briefing for practical implementation and risk coverage.
Get the Weekly Briefing