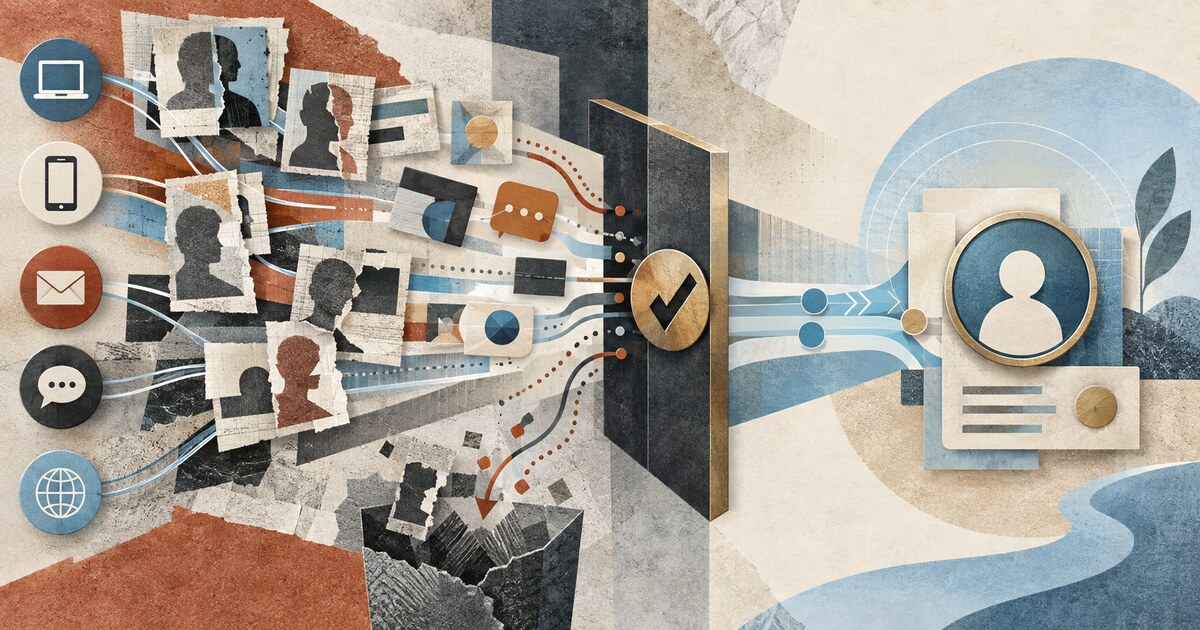
Artificial intelligence is reducing the people and resources needed to run large-scale investment, romance and impersonation scams, the president of the Financial Action Task Force has warned. Giles Thomson told the Financial Times that generative tools can help small groups create fake websites, deepfake video and targeted messages, then operate across languages and jurisdictions.
The September 14 interview extends a priority FATF set earlier this year. The intergovernmental body sets global standards for combating money laundering and terrorist financing; it does not directly supervise U.S. credit unions. Thomson's warning is therefore not a new U.S. rule or a deadline. It is an operating signal: scam capacity is becoming cheaper to assemble while the time available to verify a member, interrupt a payment and recover funds remains short.
FATF's February paper on cyber-enabled fraud found that 156 jurisdictions—90% of those assessed—identified fraud as a major money-laundering risk. It describes phishing, AI-generated deepfakes and messaging platforms as parts of a wider system that also depends on money mules, rapid payment movement and cross-border laundering. That frame matters for credit unions because a convincing synthetic message and a suspicious transaction are often handled by different teams.
Put the member report and the transaction on one clock
A member who reports a fake investment adviser, family emergency or account-takeover attempt may reach the contact center before an automated transaction model creates an alert. Credit unions should make that report immediately visible to fraud operations, payments and BSA/AML teams, with a common case identifier and a timestamped decision path.
The measures should follow the money: time from first report to account protection, time to a hold or recall request, value prevented, value recovered, referrals for financial-crime review and repeat losses tied to the same receiving account, device or beneficiary. False-positive friction belongs in the same dashboard. A faster process that repeatedly blocks legitimate members is not an effective control.
This approach builds on the value of shared intelligence. A recent credit-union fraud network showed how transaction signals can be pooled across institutions. The next step is to connect those network indicators with member-service evidence and recovery actions instead of treating detection as the finish line.
Verify outside the channel the scammer controls
Deepfake detection can help, but it should not become the only test for a voice or video request. A credit union needs step-up verification that changes the channel and the evidence: call a trusted number already on file, require an authenticated session, apply a cooling-off period to a new beneficiary or route an unusual instruction to a trained employee.
Those steps should be triggered by behavior and payment context, not by age or a vague assumption about who is vulnerable. The digital-identity guidance for customer identification offers a useful parallel: new identity technology can support an existing program, but it does not replace a credit union's duty to form a reasonable belief about the person and the transaction in front of it.
Fraud teams should also test how a scam crosses channels. A tabletop exercise can begin with a synthetic video sent to a member, continue with a phone call to the contact center and end with an instant payment to a newly added recipient. The test should expose who can pause the transaction, who contacts the member, who asks the receiving institution for help and when the case becomes relevant to BSA monitoring or a suspicious activity review.
Design the anti-scam center as a workflow
FATF's February paper points to national anti-fraud centers and public-private partnerships that combine reporting, intelligence, investigation and asset recovery. Its July 1 presidency roadmap makes fraud a central priority and calls for stronger cross-border cooperation, faster transaction suspension and more effective asset recovery.
A credit union cannot create that ecosystem alone, but it can make its part interoperable. Case records should preserve the original member report, verified contact points, transaction data, receiving-account details, device or session indicators, intervention decisions and recovery requests. Sharing must stay within applicable privacy, BSA and information-sharing authorities; the answer is a defined escalation path, not informal disclosure.
Leaders should ask whether fraud, payments, member service and BSA teams can act from the same facts within minutes. If the answer depends on email handoffs, separate spreadsheets or a specialist who is off shift, AI-enabled scams will exploit the gap. The practical response is not a more dramatic warning banner. It is a rehearsed operating system that moves a credible member signal into verification, payment intervention, recovery and financial-crime review before the money disappears.
Follow the operating evidence. Subscribe to the CreditUnionAI Weekly Briefing for practical AI, fraud and technology-governance coverage.
Get the Weekly Briefing