Credit unions should treat account recovery as a distinct operating event, not a weaker version of normal authentication. The recovery record should show why the member could not use an existing authenticator, what identity evidence was evaluated, which automated risk signals were produced, who approved any exception, when a new authenticator was bound, which notifications were sent and what monitoring followed.
This is a control design, not a new credit-union regulation. AI can compare submitted evidence, flag device or behavior changes, summarize prior contacts and route a case. It should not silently accept a voice match, override a conflicting signal or replace the employee accountable for a high-risk recovery decision.
The urgency is practical. An America's Credit Unions advisory published October 29 urges institutions to review member identity-verification protocols as AI-enabled attacks accelerate. The boundary to protect is the fallback path: an attacker who cannot pass ordinary authentication may try to persuade staff to reset the very controls that stopped the login.
Separate authentication, rebinding and recovery
The NIST Digital Identity Guidelines distinguish account recovery from replacing a password when the subscriber can still authenticate with another bound factor. Recovery begins when the member no longer controls the authenticators needed for the required assurance level.
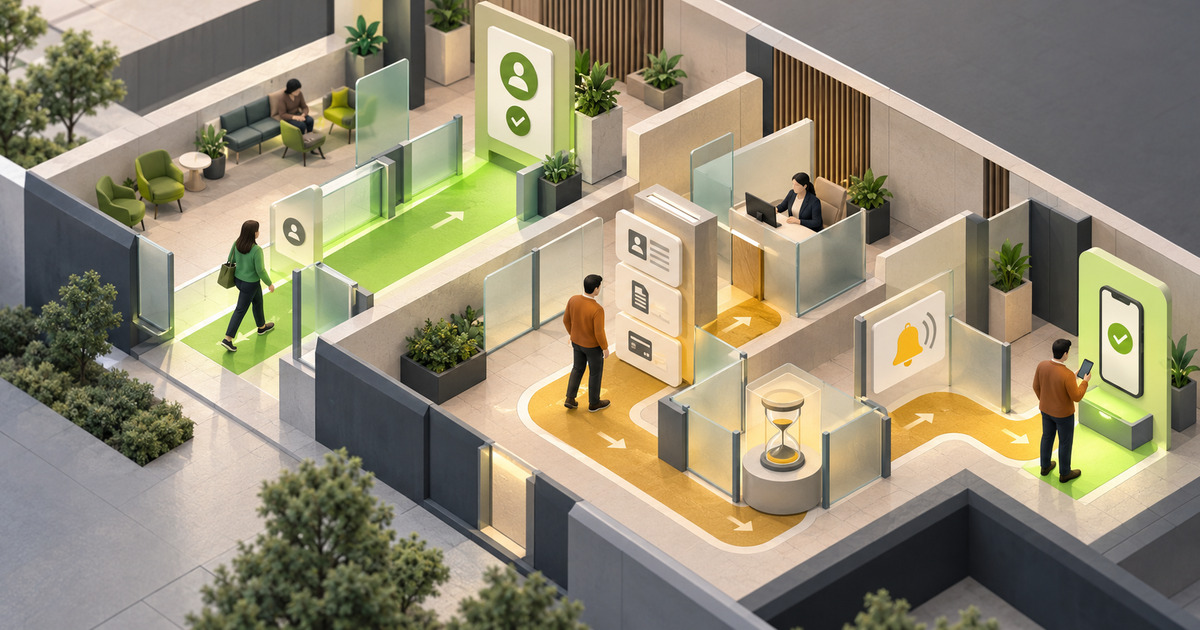
That distinction should determine the workflow. A routine login event records the factors used and the access decision. An authenticator-rebinding event records an already-authenticated member adding or replacing a factor. A recovery event records a member who cannot meet the normal authentication threshold and therefore needs a separately approved path.
Keeping the events separate prevents a contact-center workaround from appearing as an ordinary password reset. It also allows leaders to measure how often the fallback path is used, which channels originate it and which verification methods produce later fraud, complaints or rework.
Build the record around evidence and authority
Each recovery case should capture the account and channel; trigger reason; unavailable or compromised authenticators; evidence presented; device, telephone, location and behavior signals; model or ruleset version; discrepancies; employee reviewer; required second approval; decision; any delay; new authenticator; prior-authenticator invalidation; notification destination and delivery result; and post-recovery restrictions or monitoring.
The FFIEC authentication guidance says reliable identity verification generally should not depend solely on knowledge-based questions. It also directs management to evaluate authentication controls across consumers, employees, service accounts, applications and devices according to risk.
That means an AI-generated summary cannot become the evidence. The record should retain the underlying document, verified contact, device signal or recovery code that supported the decision. If an employee overrides a mismatch, the exception should name the approved authority, reason, compensating control and expiration.
Do not let deepfakes turn liveness into certainty
A FinCEN deepfake alert identifies inconsistent documents, profile mismatches, unusual IP addresses and attempts to avoid live checks as signals that warrant added scrutiny. FinCEN also notes that live audio or video can help but is not conclusive because attackers may generate synthetic responses.
Credit unions should therefore combine independent evidence rather than stacking versions of the same evidence. A voice, video and selfie generated from one stolen identity are not three independent factors. Higher-risk recovery can require a prearranged recovery method, repeated identity proofing, an existing bound factor, a known-device confirmation or an in-person step, depending on the member and transaction risk.
Bind the new factor, notify and watch
NIST recognizes saved or issued recovery codes, prearranged recovery contacts and repeated identity proofing as recovery methods. It also requires an account-recovery notification. A credit union should record both the notification attempt and its delivery result through a destination that the recovery event did not silently replace.
High-risk cases may also need a delay or temporary restriction before a new factor can authorize profile changes, external transfers or new payees. The evidence record should state when the restriction begins, what action releases it and who may shorten it.
Useful measures include recoveries by channel and reason, automated flags by disposition, override rate, second-review rate, notification failures, time to restore access, member abandonment, repeat recovery, post-recovery profile changes, fraud losses and complaints. False positives matter too: an overly rigid recovery path can exclude members who changed devices, lost access to a phone number or need an accessible alternative.
Our digital-credentials reporting explains how verified credentials can support existing identity controls. The complaint-analysis controls show how to connect a failed access decision to member remediation and root-cause review.
The control objective is simple: the recovery path may be slower than normal login, but it should never be less accountable.
Follow practical fraud and identity controls. Explore published CreditUnionAI Weekly web briefings for source-backed operating coverage.
Browse web briefings