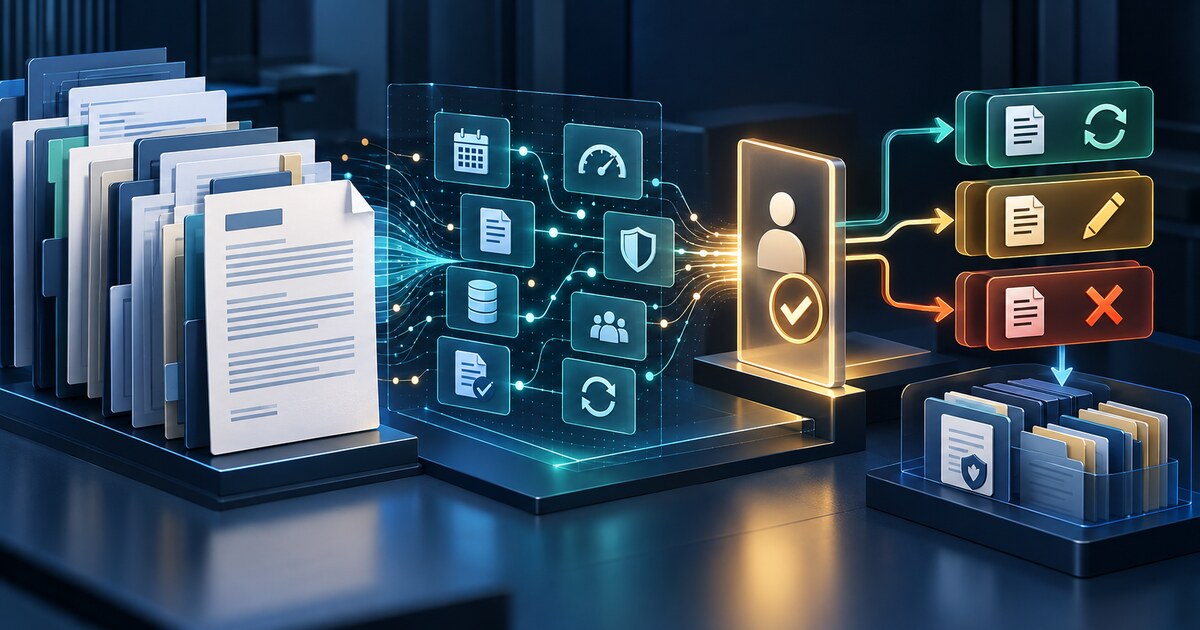
Contract monitoring is a practical credit-union AI use case because the work is scattered across executed agreements, amendments, service reports, invoices, incident records, audit reports and email. A system can locate clauses, extract dates, link obligations to evidence and warn when a notice or renewal window is approaching.
The shortcut to avoid is treating extracted text as a legal conclusion or a vendor-performance verdict. Defined terms, amendments, order forms and incorporated documents can change the meaning of a clause. A service-level report may also show that a target was met while member harm, repeat incidents or unresolved control gaps tell a different story.
The NCUA’s third-party relationship guidance says the depth of planning, due diligence and controls should reflect the credit union’s risk profile and the relationship. The agency’s AI resource, updated April 28, 2026, says existing technology-neutral requirements continue to apply and highlights vendor due diligence, internal controls and ongoing risk monitoring. The FFIEC’s outsourced technology resilience guidance emphasizes that responsibility for critical outsourced operations remains with the financial institution. The NIST AI RMF Playbook calls for regular monitoring and documentation of risks and benefits from third-party AI resources. Together, those sources support automation that strengthens oversight—not automation that substitutes for accountable contract and risk decisions.
1. Establish the authoritative contract set
Begin with a controlled inventory of executed agreements, amendments, statements of work, order forms, schedules, exhibits and incorporated policies. Record the legal entity, covered service, business owner, contract owner, criticality, location of the executed copy and hierarchy among documents. Drafts and unsigned proposals should be visibly separated.
Make the system stop when the document set is incomplete or conflicting. It should never infer that the latest filename is the governing version. For each extracted obligation, retain the source document, page or section, execution date and content hash.
Evidence: contract inventory, executed-status check, document hierarchy, amendment chain, source citation, retrieval time and content hash.
2. Separate extraction from interpretation
An AI tool may propose that language describes a renewal date, service level, audit right, data-use restriction, insurance requirement, breach notice, subcontractor condition or termination right. It should label that output as a candidate until legal, procurement, vendor-management or the designated business owner confirms the meaning.
Require a confidence indicator and a reason for uncertainty. Defined terms, cross-references, exceptions and incorporated documents should route to review. Prohibit the model from converting “commercially reasonable,” “material,” “promptly” or similar judgment language into a precise rule unless an accountable reviewer documents the interpretation.
Evidence: extracted text, proposed obligation type, cited definition and cross-reference, uncertainty flag, reviewer interpretation and approval date.
3. Turn each obligation into an owned control
Map confirmed obligations to a person, due date, evidence source, escalation path and dependency. A vendor’s obligation to maintain insurance, deliver an audit report or notify the credit union of an incident needs a recipient and a response workflow. A credit union obligation to provide notice before non-renewal needs a calendar trigger and authorized decision maker.
Do not track dates alone. Link service levels to operating metrics, data restrictions to data flows, security terms to assurance reviews, business-continuity commitments to test results and pricing terms to invoices. One clause may require several controls; one control may satisfy several contracts.
Evidence: obligation identifier, owner, trigger, due date, control link, evidence location, dependency and escalation rule.
4. Reconcile contract promises with operating evidence
Feed the monitoring process approved evidence rather than vendor summaries alone. Relevant inputs can include uptime records, incident tickets, recovery tests, complaint trends, invoice adjustments, audit reports, penetration-test summaries, insurance certificates, subcontractor notices and unresolved remediation items.
Define how conflicts are handled. If the vendor dashboard reports availability within target but member-facing channels show an outage, open an exception rather than choosing one source. Track recurring near misses, waived breaches and service credits separately; a credit may satisfy a remedy without eliminating the operational risk.
Evidence: source-system record, measurement definition, reporting period, reconciliation result, exception owner, vendor response and closure proof.
5. Control changes, notices and renewal clocks
Monitor amendment requests, product changes, pricing updates, policy notices, new subprocessors, data-location changes and altered service dependencies. Compare each notice with the governing contract and the credit union’s approved risk assessment. Route material changes through the same authority used for the original decision.
Calculate notice and renewal milestones from confirmed contract terms, then add internal decision lead time. A 90-day non-renewal window may require analysis months earlier if migration, member communication, board reporting or a replacement procurement is involved. Test timezone, holiday and delivery-method rules; a calendar alert is not proof that valid notice was given.
Evidence: notice received, contract comparison, impact assessment, decision deadline, notice method, delivery confirmation and resulting amendment or disposition.
6. Keep renewal, renegotiation and exit decisions human
Use the system to assemble a decision packet, not to select the outcome. The packet should combine contractual performance, control exceptions, member impact, concentration and substitutability, total cost, future requirements, unresolved remediation, transition readiness and the consequences of automatic renewal.
Define approval authority by criticality and decision type. A routine low-risk extension may follow a delegated path; renewal of a critical core, payments, identity, AI or cloud provider may require executive, committee or board visibility. Document dissent and conditions. If evidence is incomplete, the system should propose a hold or escalation—not manufacture a recommendation.
Evidence: decision packet, alternatives considered, risk acceptance, negotiation objectives, approvals, conditions, final notice and transition trigger.
7. Preserve the audit trail and manual fallback
Retain the source documents, extraction, reviewer corrections, obligation map, performance evidence, alerts, decisions, notices and superseded records. Monitor the AI layer for missed clauses, false obligations, stale versions, citation failures and changes in reviewer-correction rates. A model or prompt change should be tested against a representative contract set before release.
Maintain a manual calendar and owner roster for the most critical contracts. Test whether staff can identify an approaching deadline, retrieve the executed agreement, assemble current performance evidence and issue a valid notice when the AI service is unavailable. Stop automated monitoring when the authoritative set cannot be proven, citation failures rise or deadlines are missed.
Evidence: immutable event history, model and workflow version, correction metrics, manual calendar, fallback exercise, stop decision and restart approval.
A minimum renewal-decision packet
Procurement, vendor-management, legal and operations leaders should be able to review one compact packet containing:
- the complete executed contract set and the confirmed notice and renewal terms;
- the obligation map with owners, dates, control links and open exceptions;
- service, security, resilience, data-use, financial and member-impact evidence;
- material notices, amendments, subprocessors and unresolved remediation;
- total cost, service credits, concentration and transition estimates;
- renew, renegotiate, hold and exit alternatives with accountable approvals; and
- the notice, implementation or transition plan plus retained proof of delivery.
The packet should make three separate questions visible: What did the contract require? What happened in operation? What decision is authorized now?
Run five tests before launch
- Document test: place a conflicting draft beside the executed agreement and confirm the system refuses to treat the draft as authoritative.
- Clause test: split one obligation across a definition, schedule and amendment and verify that the complete meaning routes to a reviewer.
- Evidence test: create a disagreement between a vendor dashboard and member-facing incident data and confirm an exception opens.
- Deadline test: test automatic renewal, notice delivery and internal lead-time rules across weekends and holidays.
- Authority test: attempt to renew a critical agreement without the required decision packet and approvals, then repeat the cycle with the AI service unavailable.
AI can make the contract portfolio searchable and keep obligations visible between annual reviews. The durable design keeps executed documents authoritative, makes every interpretation reviewable, connects promises to operating evidence and reserves consequential vendor decisions for accountable people.
Turn contract data into decision evidence. Explore published CreditUnionAI Weekly web briefings for practical implementation and risk coverage.
Browse web briefings