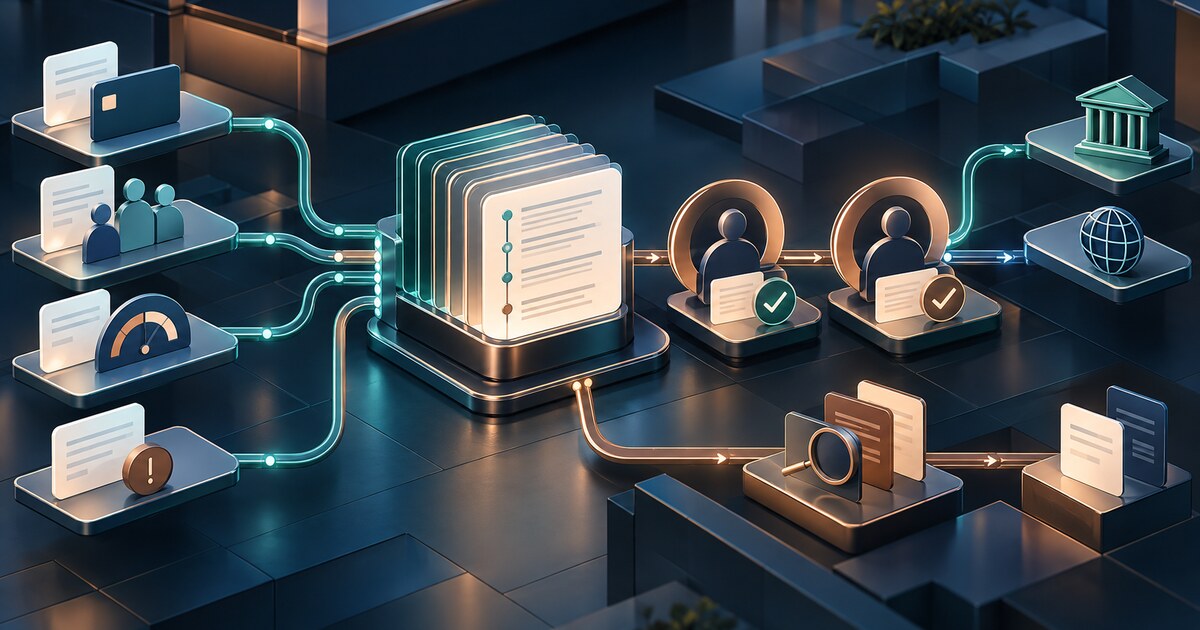
AI-assisted small-business servicing should maintain one exception ledger from the first request through the downstream change and its later review. The ledger should show who requested an action, what authority was verified, which account or cash-management service was affected, what the AI system produced, who approved or rejected the action, what changed in production and how any exception closed.
This is a control design, not a new legal standard. AI can classify messages, compare documents, summarize account history, prioritize work and draft a service note. It should not silently decide that an employee may be added, a payment limit increased, a vendor destination changed or unusual activity accepted.
The NCUA’s current AI resources emphasize vendor due diligence, data protection, operational resilience, model risk and ongoing monitoring. The FFIEC customer-due-diligence procedures also call for clear responsibility when a customer risk profile changes. A servicing ledger connects those expectations to the work queue.
Start with the business relationship baseline
The account-opening record should feed the servicing record, but the two are not the same. The baseline includes the legal entity, owners and controlling person, authorized signers, approved administrators, expected activity, services enabled, limits, contact channels and open conditions. Each servicing event should reference the exact baseline version in effect when the request arrived.
A change request then creates a new event, not an overwritten profile. The event identifies the requester and channel, the requested action, the affected service, verified authority, supporting evidence, risk signals, AI output and model or ruleset version, human reviewer, final decision, downstream system confirmation and post-change monitoring period.
Route authority and exposure exceptions separately
Not every mismatch is the same. An authority exception concerns whether the requester may act: a new administrator, stale resolution, disputed signer or contact-channel mismatch. An exposure exception concerns the proposed change: a higher ACH limit, new wire template, remote-deposit capability, payee change or activity outside the relationship’s expected pattern.
Separating those lanes prevents a clean identity check from being mistaken for approval of the underlying risk. It also allows different owners and service levels. Operations may resolve a document defect, treasury management may assess a limit request, BSA/AML may review an activity shift, and information security may investigate a compromised channel.
Preserve dual control and secure exception handling
Nacha’s 2026 risk-management guidance highlights dual control and independent verification when payment instructions change. Its exception-resolution bulletin recommends secure electronic channels for sensitive documents and account information.
The ledger should therefore distinguish recommendation from release. One employee or system may assemble evidence and propose a disposition; an authorized second control releases a high-risk change. The release record should include the approved value, effective time and confirmation from the system of record. Email, chat or a generated summary is not the confirmation.
Measure closure quality, not only queue speed
A faster queue can hide weaker decisions. Useful measures include exceptions by type and channel, percentage resolved without rework, aging by risk, approval and rejection rates, downstream confirmation failures, overrides, repeat requests, post-change fraud or loss, complaints and cases reopened by monitoring.
The NIST AI RMF Playbook recommends audit histories, documented human oversight, policy exceptions and escalation records. For a credit union, that means retaining both the AI recommendation and the human disposition—including when the employee disagreed, what evidence changed the outcome and whether the system later proved useful or misleading.
Our business-onboarding evidence record covers the account-opening boundary. The complaint-analysis controls show how to preserve remediation and root-cause evidence when servicing outcomes reach members.
Follow the operating evidence. Explore published CreditUnionAI Weekly web briefings for practical operations, risk and member-service coverage.
Browse web briefings